
Standards & frameworks
From gap assessment through implementation to audit readiness for ISO/IEC 27001 and the standards built on it, plus the CIS Controls and NIST CSF.
Thai regulatory compliance
BOT, SEC, OIC, SET, the Cybersecurity Act and PDPA, mapped to a concrete plan. Where a regulator requires a test, our own testing team does it.
Managed Security Services
Vendor-neutral help to select and run security projects: infrastructure improvement, security solution deployment, IT operations and IT support.
Because our consultants come from the same team that runs penetration tests and red team engagements, the roadmaps we build are shaped by what we have seen break in the field. We turn a stack of findings into a prioritised plan that a team can deliver. We act as a vendor-neutral advisor alongside your internal teams.
Security Standards & Frameworks
We help organisations reach and maintain the standards their customers, regulators, and partners expect: from gap assessment through implementation to audit readiness.
Information security & governance
- ISO/IEC 27001: the certifiable standard for an Information Security Management System (ISMS). We help you build, document, and maintain the ISMS that most other standards on this list extend.
IT service & business continuity
- ISO/IEC 20000-1: the IT Service Management System (SMS) standard, aligned with ITIL practice. For teams that need service delivery to be formal, measurable, and auditable.
- ISO 22301: the Business Continuity Management System (BCMS) standard. We help you run the business impact analysis and build the plans that keep operations running through a disruption, the kind of preparation the 2025 earthquake made concrete for many Thai businesses.
Privacy
- ISO/IEC 27701: the Privacy Information Management System (PIMS), an extension of ISO/IEC 27001 (which must be in place first). Covers both controller and processor roles.
- ISO/IEC 27018: a code of practice for protecting personal data (PII) when you act as a processor in a public cloud.
Cloud
- ISO/IEC 27017: a code of practice for cloud-specific security controls. Adopted within your ISO/IEC 27001 ISMS rather than certified on its own.
- CSA STAR: the Cloud Security Alliance assurance program built on the Cloud Controls Matrix (CCM). Level 1 is a self-assessment; Level 2 is a third-party certification that builds on ISO/IEC 27001.
AI
- ISO/IEC 42001: the first international AI Management System (AIMS) standard, published in 2023. For organisations that develop or use AI and need governance, risk, and lifecycle controls around it.
Control frameworks
- CIS Critical Security Controls: a prioritised, globally accepted set of defensive actions that stop the most common and damaging attacks first, developed by a community of IT experts drawing on first-hand experience as cyber defenders.
- NIST CSF: a risk-based framework for organising and maturing a security programme across identify, protect, detect, respond, and recover.
Certification itself is issued by an accredited certification body; our role is advisory and implementation support that gets you ready to pass. We hold ISO/IEC 27001 ourselves (certified across our own consulting, testing, and training services), so the guidance comes from a team that has sat on the other side of the audit. ISO/IEC 27017 and ISO/IEC 27018 are codes of practice implemented within an ISO/IEC 27001 ISMS, not certifications awarded on their own.
We map your current state and your roadmap to these standards, so progress is measurable and auditable, and so you can demonstrate to auditors and partners exactly where you stand. If your programme needs evidence in a specific format, tell us during scoping.
Regulatory compliance (Thailand)
Thai organisations answer to sector regulators as well as international standards, and most of those regulators mandate exactly the security testing and governance our team already performs. We map your obligations to a concrete plan. Where a regulator requires a penetration test, vulnerability assessment, or source code review, our own testing team does the work and produces evidence in the form your regulator and auditor expect. We advise and prepare you; we are not the regulator, and we are not your auditor.
BOT
Applies to: Financial institutions regulated by the Bank of Thailand (BOT).
What it asks for: The BOT's IT-risk and cyber-resilience requirements call for a secure development lifecycle: a vulnerability assessment before a system goes live and after any significant change, penetration testing of systems connected to external networks, and source code review for critical systems (including Internet Banking and Mobile Banking).
What we do: We deliver those assessments and help you evidence them.
SEC
Applies to: Organisations under the IT governance notification of the Securities and Exchange Commission (SEC, ก.ล.ต.).
What it asks for: An independent penetration test of critical systems connected to untrusted networks (at least once every three years for the highest-criticality systems and on a longer cycle for others), plus a vulnerability assessment of critical systems at least once a year.
What we do: We perform the independent testing and prepare the report you file.
OIC
Applies to: Insurers, under the Office of Insurance Commission (OIC, คปภ.).
What it asks for: The IT security and governance expectations of the Office of Insurance Commission.
What we do: We help insurers meet those expectations, aligning your controls and testing evidence to what the sector requires.
SET
Applies to: Listed companies, under the Stock Exchange of Thailand (SET).
What it asks for: The IT governance expectations of the Stock Exchange of Thailand.
What we do: We align your security programme and testing cadence to those expectations.
NCSA
Applies to: Organisations designated as Critical Information Infrastructure (CII) under Thailand's Cybersecurity Act (B.E. 2562), overseen by the National Cyber Security Agency (NCSA).
What it asks for: Risk-assessment, testing, and incident-readiness obligations.
What we do: We support each of those obligations.
PDPA
What it asks for: Thailand's Personal Data Protection Act (B.E. 2562) is a governance obligation as much as a legal one.
What we do: We align your privacy controls to it, and pair it with ISO/IEC 27701 when you want a certifiable privacy management system on top.
Exactly which of these bind you depends on your sector and how a regulator classifies your organisation. We confirm the ones that actually apply during scoping, so the roadmap targets the obligations that apply to you.
Managed Security Services
In Thailand, many organisations are investing significantly in technology and outsourced services to transform their business. Projects often fall short when IT teams are consumed by ongoing operations and unclear executive decisions, while IT leaders still have to focus scarce resources on operations, performance, reliability and security. Use security experts to select and manage projects with a vendor-neutral approach:
- Infrastructure improvement
- Deploy security solutions
- Improve IT operations
- IT support
We operate along with your internal teams as an advisor, drawing on knowledge gained over many client engagements and IS partners. With a vendor-neutral choice of experienced SIs blended with our cyber security consultants, you can make the decision with us.
How we work
Every consulting engagement follows the same five-step process, so advice turns into action.
Scoping
We agree on what the engagement needs to achieve: a specific certification, a broad maturity uplift, or help with a particular pain point. You get a proposal with a fixed timeline and price. It states the objectives and the deliverables.
Proposal with a fixed timeline and price
Gap assessment
We measure your current state against the relevant framework (ISO/IEC 27001, the CIS Controls, or both) through document review, interviews, and hands-on inspection.
An honest picture of where you stand today
Roadmap
We translate the gaps into a prioritised roadmap: what to fix first, what can wait, and what each step costs in effort. Priorities are weighted by real risk, drawing on what our testing team sees attackers exploit, so quick wins and structural changes are both accounted for.
Prioritised roadmap with effort per item
Execution support
We work alongside your internal teams to deliver the roadmap: refining policy, selecting and deploying solutions with a vendor-neutral eye, and improving IT operations.
You get an advisor in the room
Review & advisory cadence
We reassess progress against the roadmap on an agreed cadence, adjust priorities as your environment and threats change, and keep the programme moving.
The engagement is a working relationship
What you get
Consulting is delivered as a practical programme.
Gap assessment report
An honest, framework-mapped picture of where your security stands today, written so both leadership and practitioners can use it.
Prioritised roadmap
A sequenced plan of what to fix and when, with each item weighted by real risk and scoped for effort, so your team knows exactly where to start.
Policy & documentation support
Practical help building the policies, standards, and evidence an ISMS or a control framework requires, tailored to your organisation.
Advisory cadence
Regular check-ins to track progress, adjust priorities, and keep momentum, so the programme does not stall after the report is delivered.
Vendor-neutral guidance
Recommendations on solutions and improvements made in your interest, drawing on many client engagements and IS partners, with no product to sell you.
We do not sell security products, so "configure what you already own" stays on the table.
Team credentials
- OSCP
- OSCE
- CREST CRT
- CREST CPSA
- GIAC GREM
Advice is delivered by our in-house team holding industry certifications including those above, each earned through hands-on practical examination. The same team presents its research at international venues and has served 180+ clients across finance, enterprise, and critical sectors. That offensive background is what keeps our consulting grounded: we recommend controls because we have seen what happens when they are missing. See the full list of certifications the team holds.
Consulting works best paired with hands-on validation
Penetration test
A penetration test confirms that the controls on your roadmap actually hold.
Red team
A red team engagement tests whether your people and process respond the way the plan assumes they will.
Last reviewed: 12 Oct 2026
CONSULTING
We map your obligations to a concrete plan and confirm during scoping which ones apply. You get a proposal with a fixed timeline and price.
Frequently asked questions
Which standards and frameworks do you help us achieve?
ISO/IEC 27001 (ISMS), ISO/IEC 20000-1 (IT service management), ISO 22301 (business continuity), the ISO/IEC 27701, ISO/IEC 27017 and ISO/IEC 27018 privacy and cloud family, ISO/IEC 42001 (AI management), and control frameworks like the CIS Critical Security Controls and NIST CSF. We hold ISO/IEC 27001 ourselves. Certification is issued by an accredited body; our role is advisory and implementation support that gets you audit-ready.
Can you help us meet Thai regulatory requirements such as BOT, SEC, and PDPA?
Yes, for the Bank of Thailand, SEC, OIC, SET, the Cybersecurity Act, and PDPA. The work usually divides in two: the obligations that need a document or a process written and approved, and the ones that need a test performed and its evidence filed. Our testing team covers the second half in house, so a regulator's request for a penetration test or a code review does not become a second procurement. What we cannot be is your auditor or your regulator: we prepare you for both.
Do you sell security products?
No. The practical effect is that 'keep what you already own and configure it properly' stays available to us as a recommendation, and it is often the right one. Where a product genuinely is the answer, we help you run the selection and the project, and the licence is bought from the vendor directly.
From our consultants
ARTICLES/24 Jul 2026
Cybersecurity Compliance พื้นฐานที่นำไปใช้ได้จริง
Cybersecurity Compliance คือการสร้างกระบวนการและมาตรการด้าน Cybersecurity ที่สามารถนำไปปฏิบัติได้จริง และพิสูจน์ได้ว่าองค์กรมีการบริหารความเสี่ยงอย่างเหมาะสม
ARTICLES/19 May 2025
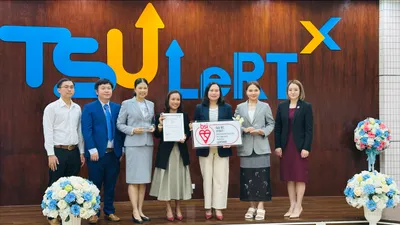
มหาวิทยาลัยทักษิณ เดินหน้าสู่ ISO/IEC 27001:2022
อินค็อกนิโตแล็บร่วมโครงการพัฒนาระบบบริหารจัดการความมั่นคงปลอดภัยสารสนเทศของมหาวิทยาลัยทักษิณ ตามมาตรฐาน ISO/IEC 27001:2022 พร้อมงาน Cyber Drill และ Pentest
ARTICLES/29 Mar 2025
บทเรียนจากแผ่นดินไหว สู่แผนรับมือด้วย ISO 22301
แผ่นดินไหวเมียนมา 28 มีนาคม 2025 ทำให้หลายธุรกิจในไทยหยุดชะงัก บทความว่าด้วยการวางแผนความต่อเนื่องทางธุรกิจด้วย ISO 22301 ให้พร้อมรับเหตุที่ไม่คาดฝัน
Tell us which standard or regulator you answer to
We confirm which obligations apply and propose a plan with a fixed timeline and price.

