Courses
Secure Software Development
A selected, interactive platform for developers to create more secure applications, covering well-known programming languages.
Security Awareness
A full set of toolkits, training contents and experienced speakers for enterprise-wide security awareness campaigns, with tailored offering packages and systematic setup support.
Social Media Investigation
Developed for law enforcement teams only. Teaches how information is collected from social media platforms including Facebook, X, Instagram, LinkedIn, TikTok and related topics, and how those channels can be exploited, with hands-on exercises and demonstrations of attacker techniques. Built around the platforms and techniques investigators actually encounter, to help units operate more effectively.
Taught by practising pentesters
- The best security training comes from people who break systems for a living. Our courses are built and delivered by the same team that runs penetration tests and red team engagements, so what you learn in the room reflects how attackers actually operate today.
We have taught developers to write safer code, helped enterprises run organisation-wide awareness campaigns, and built tailored programmes for law enforcement units. Every course is shaped around the audience in front of us. Our team of experienced penetration testers provides customised content and organisation-specific materials, combining theoretical and practical knowledge.
How we work
Every training programme follows the same five-step process.
Needs assessment
We start by understanding who is in the room and what they need to walk away able to do: the team's current skill level, the technologies they work with, and the specific risks their roles carry. The proposal states the audience, the outcomes, and the duration.
Proposal stating audience, outcomes and duration
Curriculum design
We build the syllabus around those outcomes, mapping each module to a concrete skill and weighting theory against hands-on practice to match the group. Content is drawn from real engagements, using examples and scenarios relevant to your industry.
Syllabus built around the outcomes
Delivery
Courses are led by practising testers, so every technique taught is one the instructor has actually used. Sessions are interactive and lab-heavy, with participants working through exercises on a live platform. We deliver on-site, remotely, or in a mix that suits your team.
Exercises on a live platform
Assessment & feedback
We check that the learning landed through exercises and practical challenges during the course, and give participants feedback they can act on. You get a clear picture of where the team stands afterwards.
Feedback participants can act on
Follow-up & debrief
We close with a debrief for the sponsoring team, share materials for ongoing reference, and discuss where the next step lies, whether that is a more advanced course or an assessment to test the new skills in practice.
Materials kept for reference
Delivery
Our security awareness packages, delivered online, onsite, or hybrid, scale from a single department to an entire organisation. Sessions are scheduled around your team's availability, with tailored content, phishing simulations, and refresher modules that keep security top of mind long after the course ends.
- On-site
- Remotely
- In a mix
What you get
A programme includes:
Tailored curriculum
A syllabus built around your team's roles, technologies, and risks, using examples drawn from real engagements.
Hands-on labs
Practical exercises on a live platform, so participants build muscle memory.
Organisation-specific materials
Course content and reference materials customised to your environment, kept for the team to use after the session ends.
Practical outcomes
Participants leave able to apply specific skills: developers who can spot and fix a class of vulnerability, staff who can recognise a phishing attempt, investigators who can gather evidence from social platforms.
Debrief for sponsors
A summary for the team that commissioned the training, covering what was delivered and where the group stands.
Years of experience conducting classes in Thailand and internationally.
Team credentials
- OSCP
- OSCE
- CREST CRT
- CREST CPSA
- GIAC GREM
Courses are designed and delivered by our in-house team holding industry certifications including those above, each earned through hands-on practical examination. The same team presents its research at international venues and has served 180+ clients across finance, enterprise, and critical sectors. See the full list of certifications the team holds.
Our training draws on the same methodology that underpins our testing services, which follow NIST SP800-115 (Technical Guide to Information Security Testing and Assessment), so the techniques taught reflect recognised, industry-standard practice. Where your programme supports a compliance requirement (secure-development training to satisfy an audit, or awareness training as part of a broader security programme), tell us during scoping and we will align the curriculum and any evidence of completion to what you need.
Training pairs naturally with hands-on assessment
Penetration test
Many clients follow a secure-development course with a penetration test to measure the improvement in practice.
Red team
Run awareness training alongside a red team engagement to test how the organisation responds under pressure.
Last reviewed: 12 Oct 2026
TRAINING
We start by understanding who is in the room and what they need to walk away able to do.
Frequently asked questions
Who delivers the training?
Practising penetration testers, the same team that runs our pentest and red team engagements. Every technique taught is one the instructor has actually used in the field, so what you learn reflects how attackers operate today.
Are the courses hands-on or lecture-based?
Lab-heavy and interactive. Participants work through exercises on a live platform, so they build muscle memory. We weight theory against hands-on practice to match the group, and deliver on-site, remotely, or in a mix.
Can the curriculum be tailored to our organisation?
Yes. We start with a needs assessment (who is in the room, their current skill level, the technologies they work with, and the risks their roles carry), then build the syllabus around those outcomes, using examples drawn from real engagements relevant to your industry. Materials are customised and kept for the team afterward.
Learn from our team
ARTICLES/5 Feb 2026
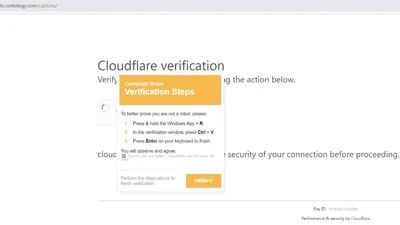
เคยเจอไหม? หน้าเว็บ Cloudflare ปลอมที่หลอกให้คุณคัดลอกคำสั่งแปลก ๆ
ClickFix และ FileFix คือเทคนิคที่หลอกให้เหยื่อลงมือทำเองโดยไม่รู้ตัว บทความอธิบายที่มา วิธีสังเกต และวิธีรับมือ สำหรับคนที่ใช้คอมพิวเตอร์ทำงานทุกวัน
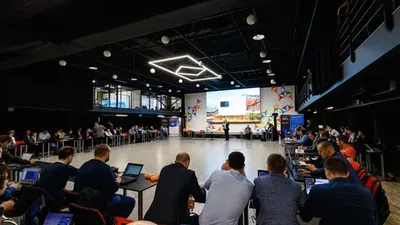
ARTICLES/26 Dec 2025
ฝึกซ้อม Cyber Drill ด้วย CYBER RANGES
ฝึกซ้อมรับมือภัยไซเบอร์ด้วย CYBER RANGES แพลตฟอร์มที่จำลองทั้งระบบและเหตุการณ์โจมตีเสมือนจริง ดูว่ามีโมดูลอะไรและใช้ซ้อมแบบไหนได้บ้าง
ARTICLES/15 Dec 2023
Cyber Skills Unleashed: Recommended Cybersecurity Learning
แนะนำคอร์สเรียน cybersecurity สำหรับคนเริ่มต้น คัดจากคุณภาพและราคาที่เข้าถึงได้จริง พร้อมเหตุผลว่าแต่ละคอร์สเหมาะกับใคร
Tell us who will be in the room
The proposal states the audience, the outcomes, and the duration.