Overview
RedAlert delivers infostealer-focused threat intelligence, continuously scanning malware logs and the dark web for credentials leaked from your employees' personal devices, customers, and third-party vendors — the blind spots that traditional endpoint protection misses. Spot and remediate compromised accounts before attackers can use them.
How we use it
We use RedAlert to watch for credentials leaking from devices an organisation does not manage — employees’ personal machines, customers, and vendors. Endpoint controls do not reach those, and stolen credentials are how a great many intrusions start.
Related Blog Posts
ARTICLES/9 Mar 2026
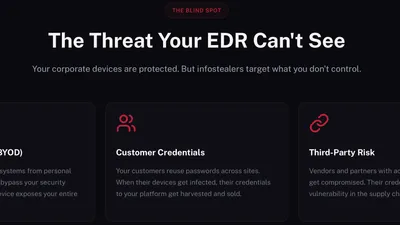
เฝ้าระวัง Infostealer Log ด้วย RedAlert
EDR ติดตั้งได้เฉพาะเครื่องที่องค์กรคุม แต่ credential มักรั่วจากเครื่องพนักงานและ outsource ที่ไม่มี agent อยู่ RedAlert หาเจอโดยไม่ต้องติดตั้งอะไร
ARTICLES/20 Feb 2026
Snowflake Breach 2024 เมื่อ Infostealer ทำให้ EDR มองไม่เห็น
กรณีศึกษา Snowflake Breach 2024 ว่า credential ที่หลุดจากเครื่องของ 3rd Party กลายเป็นทางเข้าได้อย่างไร และ Stealer Log ที่อยู่เบื้องหลังคืออะไรกันแน่