CognitoRange cyber drills built around your team's goals
Incognito LabCyber Range
CognitoRange
- cognito
- from cognition, learning
- range
- a training ground where the whole team works hands-on
Sit through a day of slides and it's gone within weeks
In CognitoRange your team investigates an incident with their own hands on real machines, one step at a time, with an instructor alongside. We design drills for organizations in Thailand such as banks, government agencies and insurers.
- Built newevery drill, around your goals
- Whole teamtrains together in one lab
- Just a browsernothing to install
A cyber drill built on an incident your organization could face
We start from one goal, say faster ransomware response, and build the incident around it.
Pick an example drill
Try it: answer question 2 with harborsync
Newcomers and veterans train in the same round Step-by-step hints keep anyone who gets stuck moving, so nobody spends half the day watching.
Written answers, read by an instructor Our instructors read and comment on each written answer about what happened and how to fix it. Your team practises the report they would send to management.
Rehearse what is close to home Scenarios follow the systems and threats your organization deals with, so what your team practises applies the next working day.
drill.example.co.th/challenges/night-harbor
COGNITORANGE CHALLENGESSCOREBOARDLIVE
Operation Night Harbor
forensics, lab, difficulty
10 / 60 pts
08:12. The port authority portal has been defaced. IIS and endpoint logs from WEB01 are in your lab. Find out how the attacker got in.
TEAM ALERT
A cyber range where every participant gets their own machines
Each team gets its own lab, built to look like the systems your people work with every day. Everyone types the commands, opens the logs and makes the calls.
Try anything, risk nothing in production Delete files, kill processes, change system settings. None of it reaches your production systems.
Make mistakes, start over at once Break a machine, spawn the set again, keep going.
drill.example.co.th/challenges/night-harbor
COGNITORANGE CHALLENGESLIVE
Lab
STOPPED- queued
- provisioning
- configuring
- running
This lab has 4 machines, all created fresh when you spawn
Start here
WKS01 10.20.3.30
user
analystpass
••••••••••The rest of the lab0 of 3 up
- WEB01 10.20.3.20RDPstopped
- SOC01 10.20.3.200VNCstopped
- DC01 10.20.3.10RDPstopped
AccessWireGuardOpenVPNBrowser
Participants bring a laptop. That's the whole setup.
Everything opens in a browser tab. Nothing gets installed on company laptops and nothing goes to IT in advance.
No waiting on IT Your IT department has nothing to prepare.
Run it anywhere A training room or everyone from home. All it needs is internet.
Every hour goes to training Sign in and start, so the first hour is already practice. Anyone who prefers their own tools can connect over VPN.
drill.example.co.th/console/night-harbor/WKS01
Lab not running. Spawn it in the lab above.
1280×600, 10.20.3.30
The score belongs to the team
The lab, the score and the progress belong to the team, so people split the work the way they would in an incident, with one person on the SIEM, one on the web server, one writing the summary.
Find coordination gaps early Who waits on whom and where handoffs slow down show up during the drill, while there is still time to fix them.
Teams across departments work together SOC, IT and system administrators share one lab and see who is doing what at every moment.
Rehearse the roles you hold in an incident Each person can take their own role, such as SOC analyst, IR lead, system administrator or reporter.
drill.example.co.th/team
COGNITORANGE TEAMLIVE
Blue Team 3
4 members, 1 live lab
1/ 3 solved
- PPloySOC analystin SOC01
- KKritIR leadin WEB01
- NNokSystem adminin DC01
- TTonReporteridle
RECENT TEAM ACTIVITY
- Nok opened the DC01 console
- Krit opened the WEB01 console
- Ploy solved question 1, +10 pts
Teams compete on a live scoreboard
With points and rival teams, people focus without being told to. The room shifts from listening to racing for answers.
Participants stay engaged all day The board moves every time a team solves something, so phones stay in pockets.
Organizers see what each team needs to work on The chart shows where each team got stuck and for how long, ready for the debrief and for planning the next round of training.
drill.example.co.th/scoreboard
COGNITORANGE SCOREBOARDLIVE
Scoreboard
4 teams, updated live
3/ 4 your rank
SCORE OVER TIME
Blue Team 1Blue Team 2Blue Team 3Blue Team 4
| Rank | Team | Solves | Score |
|---|---|---|---|
| 1 | Blue Team 1 | 3 | 60 |
| 2 | Blue Team 2 | 3 | 40 |
| 3 | Blue Team 3 (you) | 1 | 10 |
| 4 | Blue Team 4 | 1 | 10 |
Designed by people who compete in CTFs and run pentests every day
Your team trains with people who know how hard a good challenge should be and how attackers think.
As a team they placed 1st at the TCSD Cyber Security Competition 2019 and 3rd at the ASEAN Student Contest on Information Security 2019. Narawit and Suppawej also placed 3rd at STDIO CTF 2020.
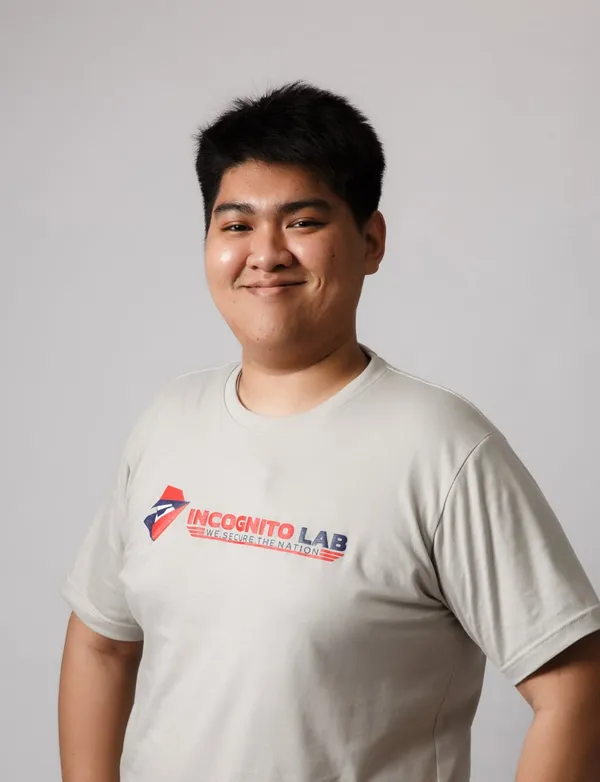
Wisawa Ploypradub
Penetration Tester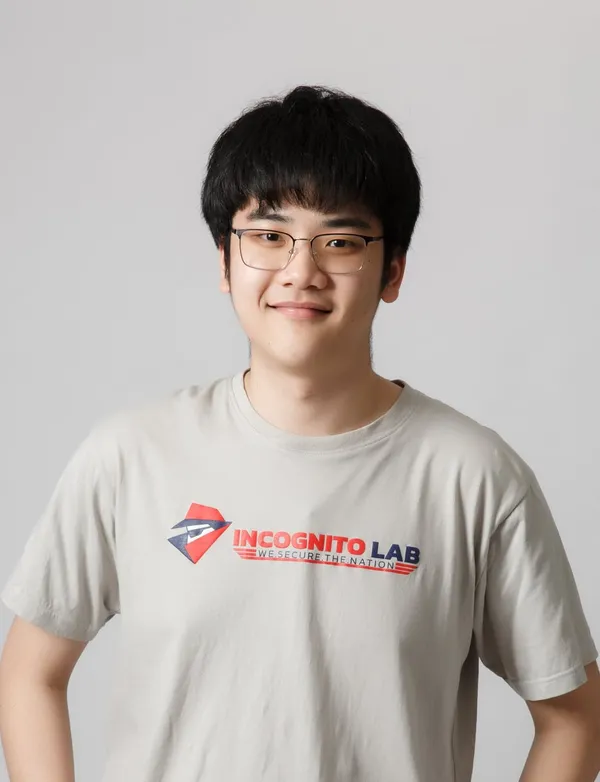
Suppawej Kerdphol
Penetration TesterWhat your organization takes away
Built new for every engagement
The incident and its questions are designed around the goals of the engagement and your environment.
Know how ready your team is
See which steps your team clears quickly and where it stalls, before an incident shows you.
Feedback from practitioners
The drill designers read your team's written analysis themselves and comment from their experience testing client systems.
Run it again to measure progress
Keep a drill and run it again with the same team or a new one, then compare rounds to see whether the team improved.
Run a drill for your team
Tell us your goals and team size, and we will design the scenario and scope.